Download Cloud and AI Security Engineer Associate.SC-500.ExamTopics.2026-10-30.99q.vcex
| Vendor: | Microsoft |
| Exam Code: | SC-500 |
| Exam Name: | Cloud and AI Security Engineer Associate |
| Date: | Oct 30, 2026 |
| File Size: | 3 MB |
How to open VCEX files?
Files with VCEX extension can be opened by ProfExam Simulator.
Purchase
Coupon: TAURUSSIM_20OFF
Discount: 20%
Demo Questions
Question 1
You have an Azure SQL Database logical server named Server1 that contains a database named DB1.
You need to configure authentication for Server1 to meet the following requirements:
SQL authentication cannot be used for any databases on Server1.
The solution must be enforced centrally at the server level.
What should you do?
- Configure a Microsoft Entra administrator for Server1.
- Enable a managed identity for Server1.
- Enable Microsoft Entra-only authentication for Server1.
- Remove SQL logins from DB1.
Correct answer: C
Question 2
You have a Microsoft Entra tenant that has the following configurations:
User consent for applications is disabled.
Only administrators can grant permissions to applications.
You register an application named App1 that uses delegated Microsoft Graph permissions.
You need to configure App1 to meet the following requirements:
Enable user sign-ins without interactive consent prompts.
Enable App1 to access Microsoft Graph on behalf of the signed-in user.
What should you do?
- Configure enterprise applications to require user assignment and assign users to App1.
- Modify the app registration to use application permissions instead of delegated permissions.
- Add the required delegated Microsoft Graph permissions to the app registration and rely on user consent during sign-in.
- Grant admin consent to App1 for the required delegated permissions.
Correct answer: D
Question 3
You have a Microsoft Entra tenant that uses Privileged Identity Management (PIM).
You need to modify the AI Administrator role settings to meet the following requirements:
Elevated access must be evaluated by another administrator before it is granted.
Privileged access must be removed automatically after a fixed period.
Which two settings should you configure? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- Expire active assignments after
- Require approval to activate
- Require justification on activation
- Expire eligible assignments after
- Activation maximum duration
Correct answer: B, E
Question 4
You have two management groups named MG1 and MG2 that contain multiple Azure subscriptions. The subscriptions are linked to a Microsoft Entra tenant.
You have a user named User1 and a global administrator named Admin1.
You are informed that User1 created an Azure subscription named Sub1 under the MG2 management group and is the only owner of the subscription.
You need to ensure that Admin1 can remove the Owner role from User1 for Sub1.
What should you do first?
- Move Sub1 to MG1.
- Assign Admin1 the User Access Administrator role for Sub1.
- Instruct Admin1 to use Privileged Identity Management (PIM) to request the Security Administrator role.
- Instruct Admin1 to enable Access management for Azure resources.
Correct answer: D
Question 5
You have a management group named MG1 that contains two subscriptions named Sub1 and Sub2.
Sub1 contains a resource group named RG-Exception and a resource group named RG1 that hosts Microsoft Foundry resources.
You need to assign an Azure policy to force new Foundry deployments in MG1 to use private endpoints. The solution must NOT restrict deployments in RG-Exception.
How should you configure the policy?
- Assign the policy to MG1 and exclude RG-Exception.
- Assign the policy to Sub1 and RG-Exception.
- Assign the policy to MG1 and RG-Exception.
- Assign the policy to Sub1 and exclude RG-Exception.
Correct answer: A
Question 6
You have an Azure key vault named KV1 that uses role-based access control (RBAC) authorization. KV1 stores database connection strings for an Azure App Service web app named App1.
You enable a firewall on KV1 and allow access to KV1 from only the virtual network that contains App1.
You need to ensure that App1 can retrieve secrets from KV1 without using credentials stored in the application configuration.
What should you create?
- an access policy for KV1
- an app registration for App1
- a private endpoint for KV1
- a managed identity for App1
Correct answer: D
Question 7
You have a Microsoft Entra tenant.
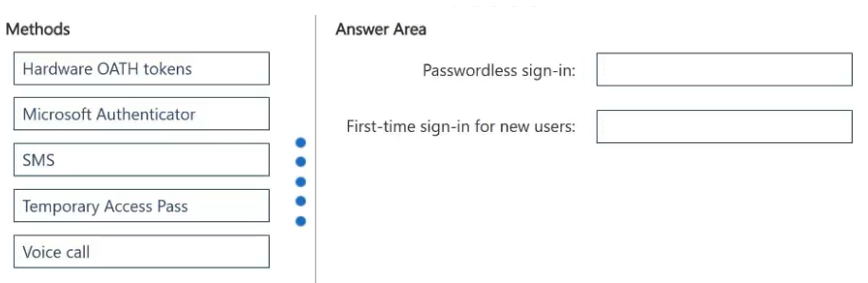
You need to implement passwordless authentication. The solution must meet the following requirements:
Users can sign in without a password by using a mobile device.
New users that sign in for the first time must use a helpdesk-issued sign-in method that expires.
Which authentication method should you enable for each requirement? To answer, drag the appropriate methods to the correct requirements. Each method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Correct answer: To work with this question, an Exam Simulator is required.
Question 8
You have a Microsoft Entra tenant that has user consent for applications disabled.
You register an application named App1 that requests the following Microsoft Graph delegated permissions:
- User.Read
- Mail.Read
You need to configure tenant permissions to meet the following requirements:
Enable users to grant consent for low-risk permissions without administrator interaction.
Ensure that applications requesting higher-privilege permissions require administrator approval.
What should you do?
- Grant tenant-wide admin consent to App1.
- Configure application assignments for App1.
- Configure Privileged Identity Management (PIM) role assignments.
- Create an app consent policy.
Correct answer: D
Question 9
You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub2. Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group1.
You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.
Which role should you assign to Group1?
- Contributor at the MG1 scope
- Contributor at the Sub1 and Sub2 scopes
- User Access Administrator at the MG1 scope
- Owner at the MG1 scope
Correct answer: C
Question 10
You have an Azure key vault named KV1 that uses role-based access control (RBAC) for data plane authorization.
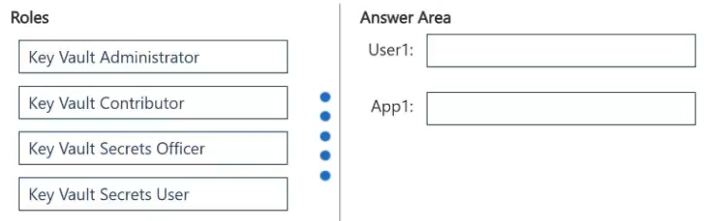
You have a user named User1 and an Azure App Service web app named App1 that has a system-assigned managed identity.
You need to configure authorization to meet the following requirements:
App1 must be able to retrieve secrets from KV1.
User1 must manage the KV1 settings without accessing secret values.
The solution must follow the principle of least privilege.
Which role should you assign to each identity for KV1? To answer, drag the appropriate roles to the correct identities. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Correct answer: To work with this question, an Exam Simulator is required.
HOW TO OPEN VCE FILES
Use VCE Exam Simulator to open VCE files
HOW TO OPEN VCEX FILES
Use ProfExam Simulator to open VCEX files
ProfExam at a 20% markdown
You have the opportunity to purchase ProfExam at a 20% reduced price
Get Now!